 R7 Orbit
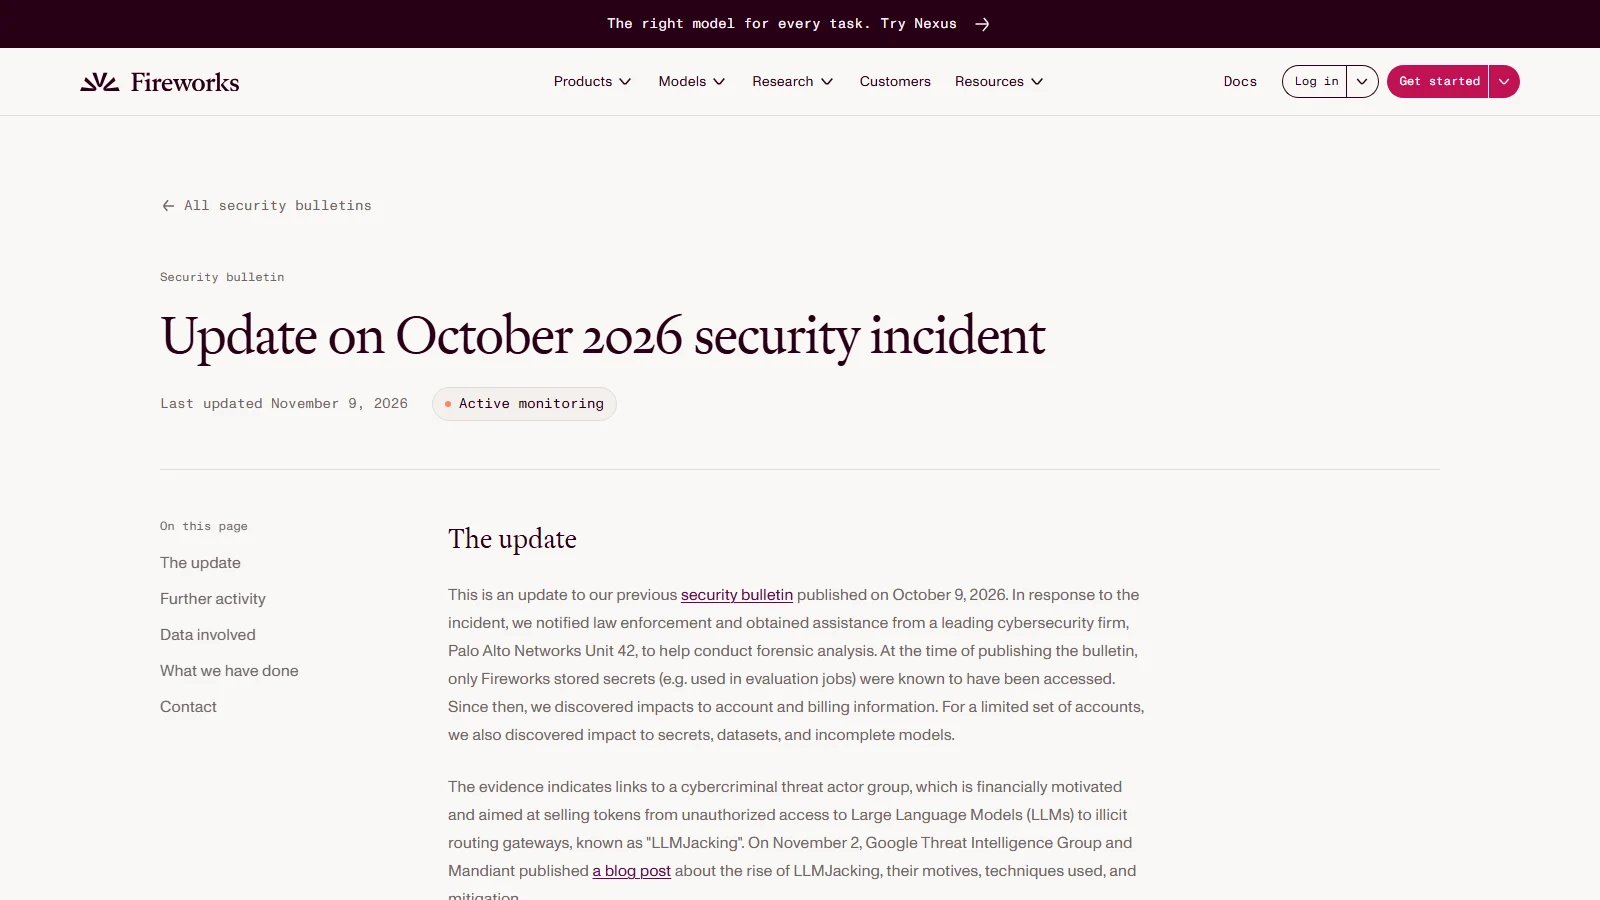
Fireworks AI, a platform for running and training AI models, said on Nov 9, 2026 that an October breach went further than it first reported. Attackers reached account and billing information, and for a limited set of accounts, stored secrets, datasets and incomplete model weights (Fireworks AI).
- Oct 6Fireworks finds misuse of internal credentials and starts containment
- Oct 9First bulletin: secrets in evaluation jobs were exposed
- Oct 23A cloud provider hosting Fireworks R&D machines has its own incident
- Oct 24The attacker uses it to reach Fireworks development machines
- Oct 25Last sign of successful access to the customer platform
- Nov 9Update widens the list of data involved
What happened
On Oct 10, Fireworks said it had found no sign that customer models, datasets or training data were touched (Fireworks AI). The update reverses part of that. Through an internal application, the attacker could see resource metadata, billing details such as addresses, invoices and credit usage, and for certain customers a subset of incomplete model weights and datasets. Fireworks says it does not store payment card numbers (Fireworks AI).
Fireworks links the attack to a financially motivated group that resells stolen access to language models through illicit routing gateways, a practice called LLMjacking. It has not named the group. It is working with Palo Alto Networks Unit 42 on the investigation and has notified law enforcement (Fireworks AI).
What changes for customers
- Paused: self-serve dataset uploads and downloads for Batch Inference and dataset-based training are off while the investigation runs.
- Not affected so far: Fireworks has found no impact on Inference, the Training SDK or Nexus, which keep no data by default.
- Notices: customers whose data was involved are being contacted directly with details and steps to take.
Source: Fireworks AI
Fireworks says the investigation is ongoing and may turn up more. It has not said how many accounts were affected.